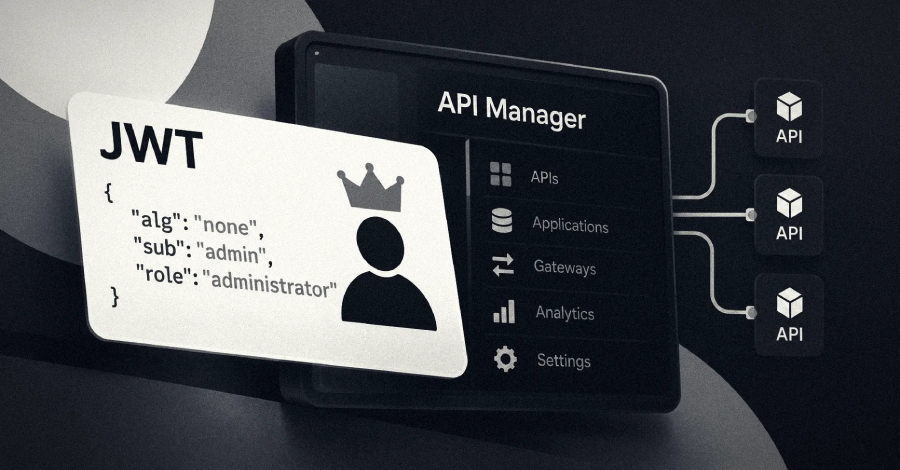
A critical security flaw in WSO2 API Manager has come under active exploitation in the wild, according to findings from watchTowr.
The vulnerability, tracked as CVE-2026-5430 (CVSS score: 9.8/10.0), is a case of improper verification of a cryptographic signature that could result in account takeover. Hacktron Team has been credited with discovering and reporting the flaw.
“JWT authentication